
DPDP consent management is the discipline of collecting, recording, honouring, and proving a person’s permission to use their personal data under India’s Digital Personal Data Protection Act, 2023. Consent is the main legal basis for processing, and Section 6(10) places the burden of proof squarely on the business. Most consent duties under the DPDP Rules, 2025 begin on 13 May 2027.
So, if your company gathers names, phone numbers, emails, locations, or payment details from people in India through a website, an app, a branch or a call centre, this guide is written for you. First, we will explain what the law actually demands. Next, we will walk through the consent lifecycle as it works on the ground. Finally, we will show how to set up a DPDP consent management platform well before the deadline arrives.
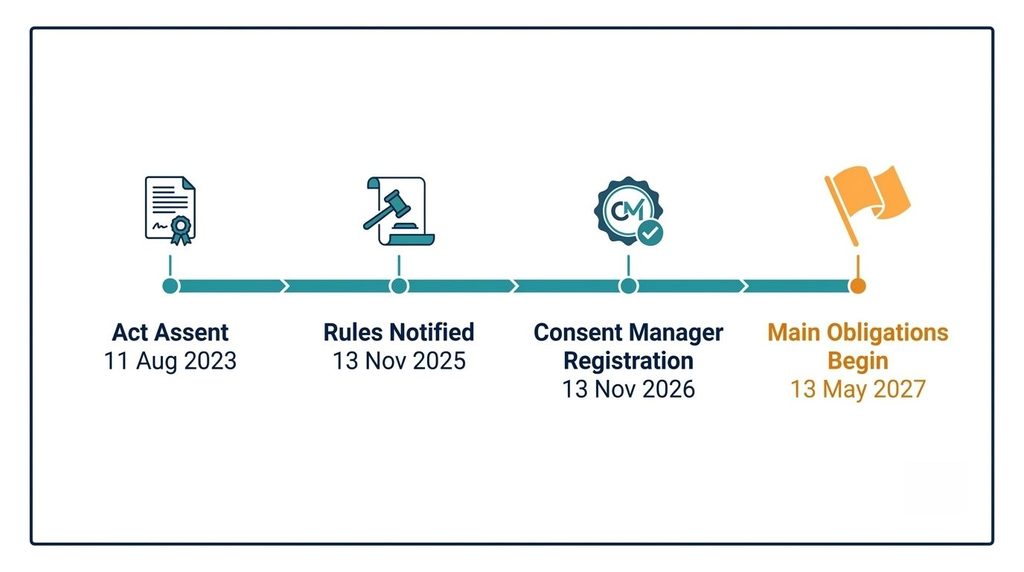
Key dates at a glance
| Date | What happens |
|---|---|
| 11 Aug 2023 | The DPDP Act, 2023 receives Presidential assent |
| 13 Nov 2025 | The DPDP Rules, 2025 are notified; provisions on the Data Protection Board take effect |
| 13 Nov 2026 | Consent Manager registration (Rule 4) takes effect |
| 13 May 2027 | Rules on notice, consent, security, breach, children’s data and Significant Data Fiduciaries (Rules 3 and 5–16) take effect |
As these dates show, the timeline is staggered rather than sudden. Nevertheless, the final and heaviest set of obligations lands on a single day in May 2027. Therefore, businesses that treat the earlier dates as a warning rather than a deadline will have a much easier time later.
Why consent suddenly matters so much
For years, Indian companies collected data through long privacy policies that almost nobody read. In practice, a single “I agree” button often covered marketing, analytics, profiling and third-party sharing all at once. However, the DPDP Act changes this habit in a fundamental way. Consent must now be specific, it must be provable, and it must be reversible.
Moreover, the financial exposure is real. As you will see in the penalties section below, the Data Protection Board can impose fines running into hundreds of crores of rupees. Consequently, consent has moved from a legal footnote to a board-level topic. In other words, it is no longer enough to “have a checkbox”; you need a system that stands up to scrutiny.
What is DPDP consent management?
Put simply, it is the combination of processes and technology that lets you answer four questions about any customer, at any moment:
- What did this person agree to?
- Which notice did they see when they agreed?
- When did they agree, and through which channel?
- Have they changed their mind since then?
To follow the rest of this guide, you first need to know the three key roles that the Act defines. The individual whose data is being handled is the Data Principal. The business that decides why and how the data is used is the Data Fiduciary. Meanwhile, any vendor that handles data on the fiduciary’s behalf, such as a CRM provider, a payment gateway or an SMS service, is a Data Processor.
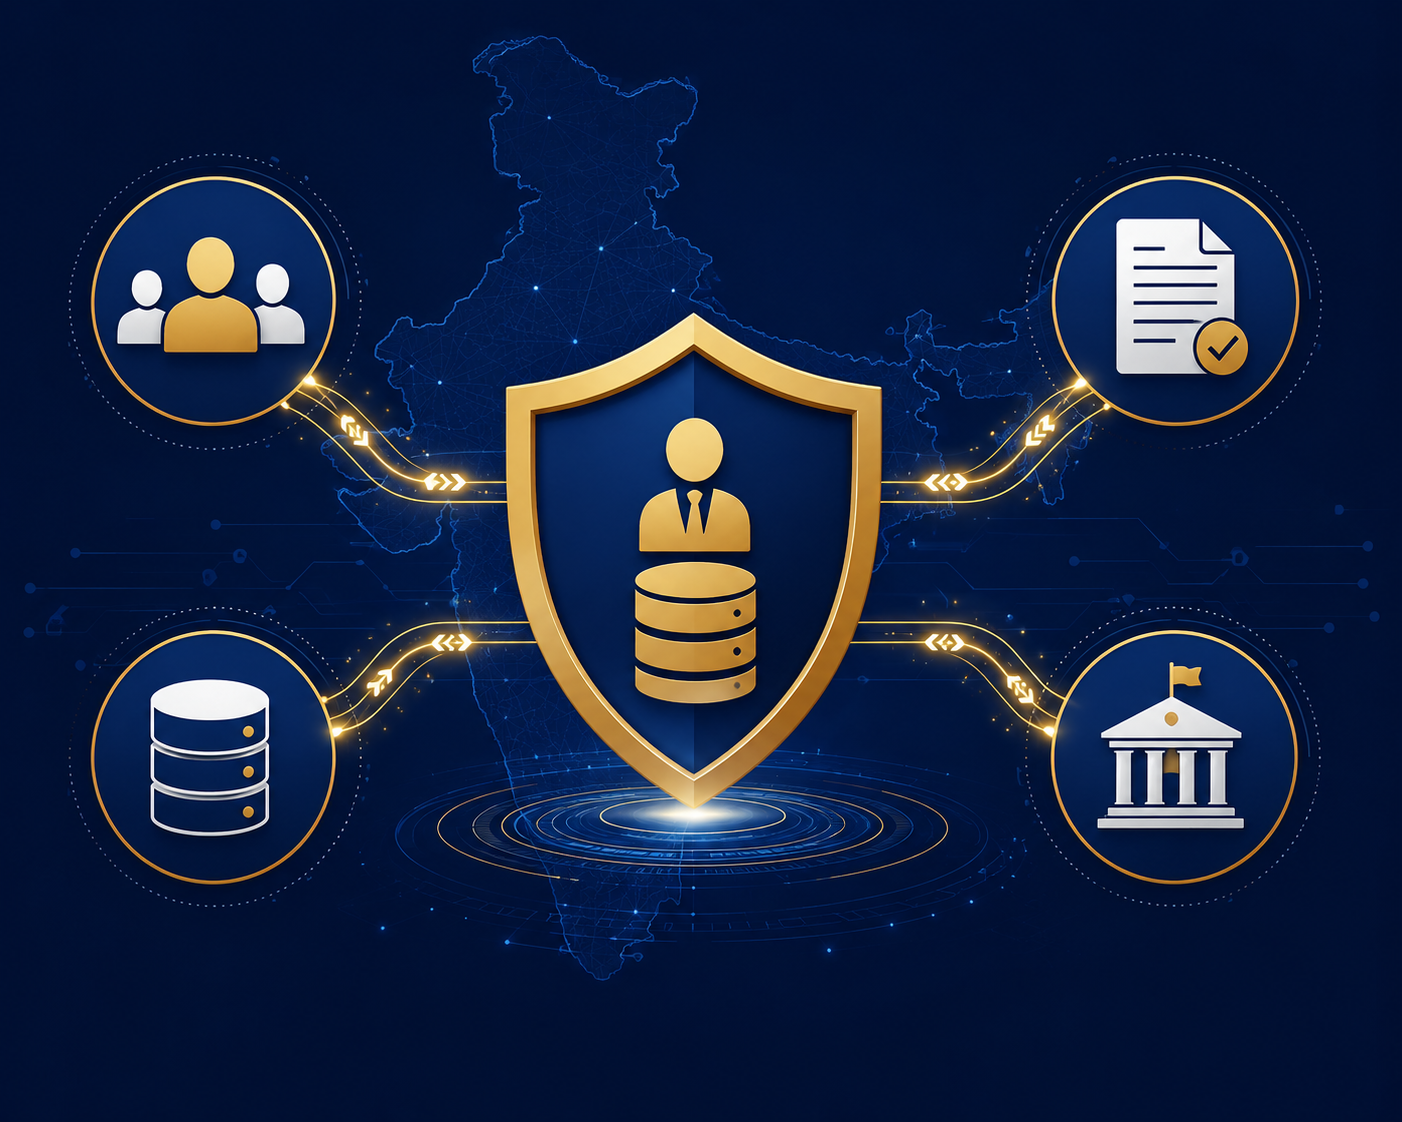
A consent management platform (CMP) is the software that a Data Fiduciary uses to run all of this. Essentially, it sits between your customer touchpoints (forms, apps, branches, call centres) and the internal systems that consume the data (CRM, marketing tools, analytics). Because of that position, it can check permission before any system acts and record every change along the way.
What makes consent valid under Section 6
Section 6(1) of the Act sets out the test for valid consent. Specifically, consent must be free, specific, informed, unconditional and unambiguous, and it must come with a clear affirmative action. Let us look at each element in turn.
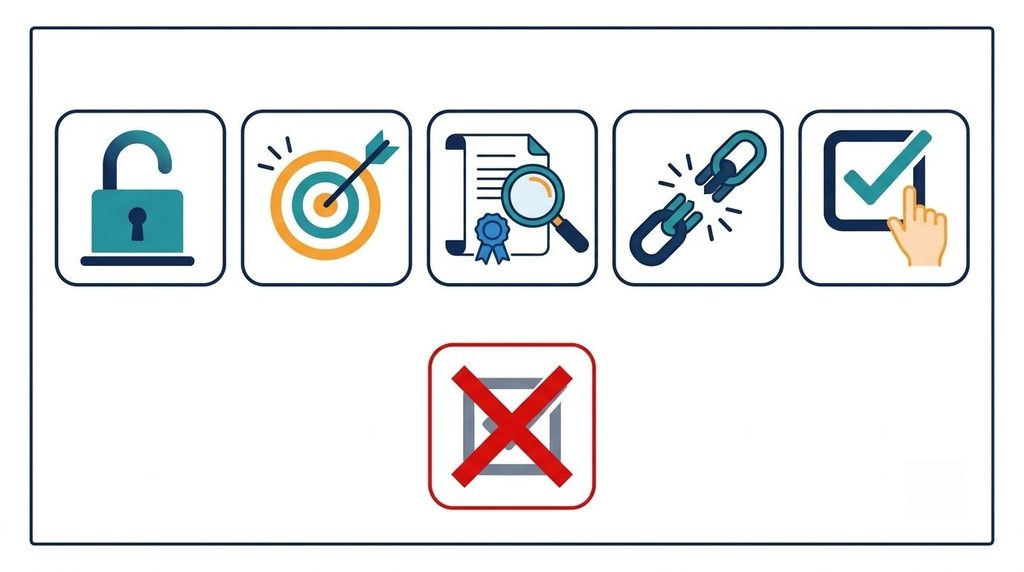
- Free: the person must not be pressured, tricked or forced to agree. Likewise, consent should not be tied to something unrelated.
- Specific: the consent must point to a stated purpose. A blanket line such as “we may use your data for business reasons” does not qualify.
- Informed: the person must give consent after reading a clear notice, not before.
- Unconditional: you cannot deny a service because someone declines a purpose that the service does not actually need.
- Unambiguous, with a clear affirmative action: a tick, a tap or an OTP counts. By contrast, a pre-ticked box or plain silence does not.
In addition, consent covers only the data that is necessary for the stated purpose. The Act itself gives a helpful illustration: a telemedicine app asks for access to a user’s phone contact list as well as her health details. Because the contact list is not needed to deliver telemedicine, her consent is limited to the data that is. Clicking “I agree” to everything does not widen the permission.
Furthermore, Section 6(2) adds a safety net. Any part of a consent that infringes the Act, the Rules or another law is invalid to that extent. For example, a clause that makes a customer waive the right to complain to the Board has no legal force, even if the customer ticked the box.
The consent notice: Section 5 and Rule 3
Every request for consent must arrive with a notice, or be preceded by one. Under Rule 3, that notice has to make sense on its own, without sending the reader to other documents. In particular, it must contain:
- An itemised description of the personal data being collected
- The specific purpose of each item, along with the goods or services it enables
- A link or method to withdraw consent, with a process as easy as the one used to give it
- Details on how the person can exercise their rights and how to complain to the Data Protection Board
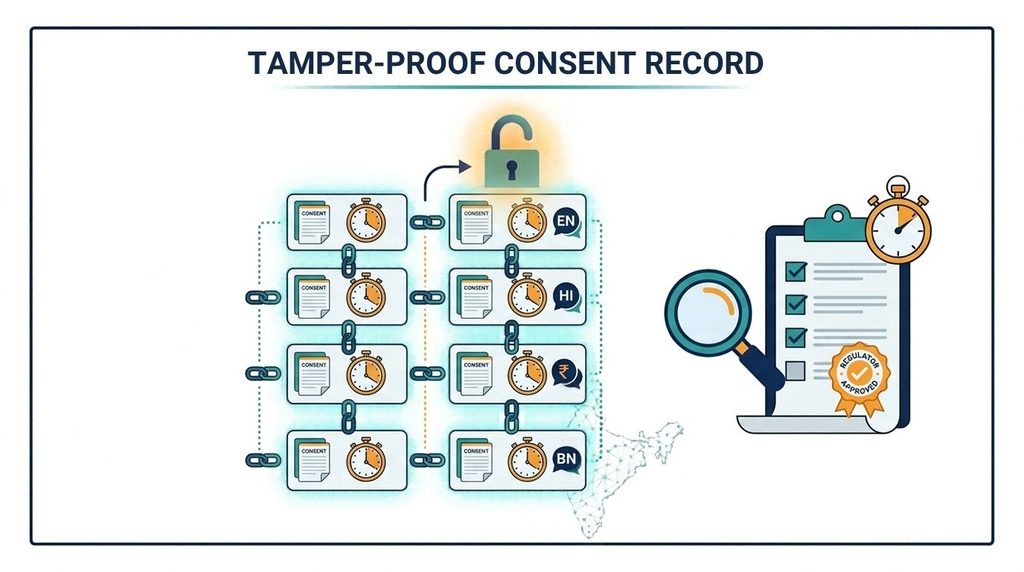
On top of that, Section 6(3) says every consent request must use clear and plain language. It must also give the person the option to read it in English or in any of the 22 languages listed in the Eighth Schedule to the Constitution. For a bank, an insurer or a telecom operator with customers across many states, this means notice templates in several languages. Equally important, each template must be versioned and stored so you can show exactly what a customer saw on a given day.
The consent lifecycle in five stages
Understanding the lifecycle makes the whole subject far less abstract. Broadly, every consent passes through five stages.
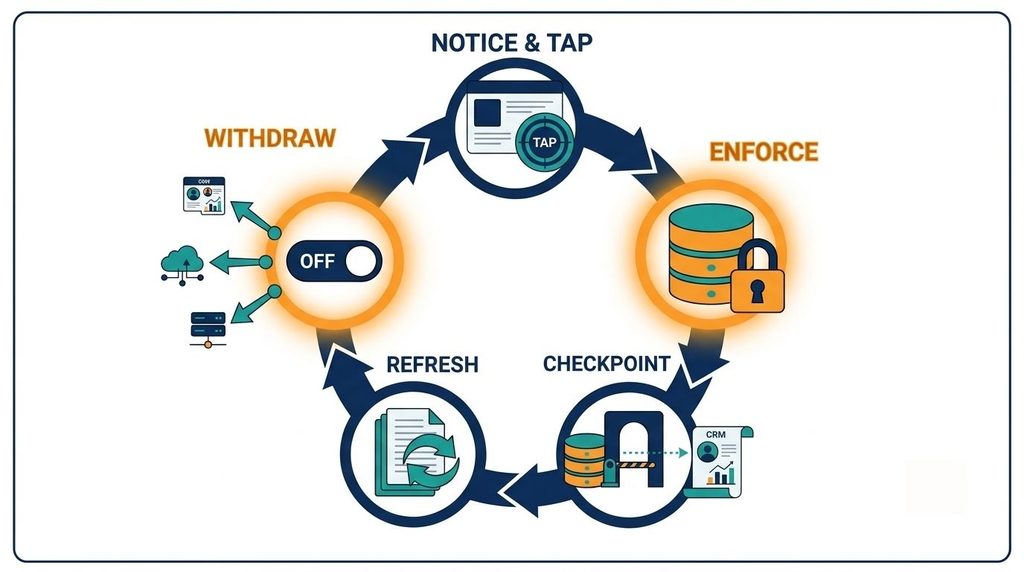
- Capture. Show the notice, record the affirmative action, and log the notice version, timestamp, channel and purpose.
- Store. Keep every consent as an individual record linked to the customer ID, in a store that cannot be quietly edited after the fact.
- Enforce. Before any system uses the data, check that a valid consent exists for that exact purpose. Marketing tools, in particular, should read from the live consent record rather than from an old export.
- Update. Whenever a purpose changes or a new product launches, collect fresh consent for the new purpose.
- Withdraw. Let the customer withdraw through the same channel with the same effort, and then stop processing everywhere, including at your Data Processors.
It is worth noting that most compliance gaps appear in stages three and five. For instance, a business may collect consent flawlessly on its website and yet keep sending WhatsApp offers from a CRM that never received the withdrawal. Consequently, enforcement and withdrawal sync deserve the largest share of your attention and budget.
Withdrawal: as easy as giving consent
Section 6(4) gives every Data Principal the right to withdraw consent at any time, and it requires the ease of withdrawing to be comparable to the ease of giving. Therefore, if consent took a single tap inside an app, withdrawal cannot require an email to a support address and a week of waiting.
After a withdrawal, Section 6(6) obliges the Data Fiduciary to stop processing within a reasonable time. It must also make its Data Processors stop. However, there is an exception: processing may continue where another law requires or authorises it. RBI, SEBI, PMLA and telecom licence rules frequently demand that certain records be retained. As a result, your system must be able to tell the difference between “stop using this data for marketing” and “delete this data entirely”. A bank, for example, may need to keep KYC records even after a customer withdraws marketing consent.
Also, remember that Section 6(5) protects past processing. Withdrawal does not make earlier, lawful processing retroactively illegal. Instead, it only stops further processing that depended on that consent. In addition, the consequences of withdrawal are borne by the Data Principal. The Act’s own illustration shows an online shopper who withdraws consent: the platform may stop letting her place new orders, but it still fulfils orders she has already paid for.
Proof of consent: Section 6(10)
Imagine a customer disputes a marketing message and claims they never agreed to receive it. Under Section 6(10), the Data Fiduciary must prove that a notice was given and that consent was obtained in line with the Act. Unfortunately, a lone tick-box value in a database row, with no history, will not hold up in front of the Board.
To be safe, keep the following for every consent event:
- The customer identifier and the channel (web, app, branch, agent or IVR)
- The notice version and the language that was shown
- The purposes consented to and the purposes declined
- The timestamp and the method (checkbox, OTP or e-sign)
- Every later change, including withdrawal, each with its own timestamp
Besides this, the Rules require Data Fiduciaries to retain certain logs for at least one year, while registered Consent Managers must keep consent records for at least seven years. Hence, retention settings should be configurable rather than hard-coded.
When you don’t need consent: legitimate uses
While consent is the main basis, it is not the only one. Section 7 lists a handful of situations in which personal data may be processed without consent. These include data that a person has voluntarily handed over for a specific purpose without objecting to its use, employment-related purposes, compliance with a law or a court order, medical emergencies, and certain functions of the State.
Crucially, these grounds are narrow. Marketing, profiling and cross-selling almost never qualify. For that reason, you should map each of your purposes to either consent or a specific Section 7 ground before you design a single consent screen. Doing so avoids both over-collecting consent and, more dangerously, relying on a legitimate use that does not actually apply.
Children’s data: Section 9 and Rule 10
Under the DPDP Act, anyone below 18 is a child. Before processing a child’s data, a business needs verifiable consent from a parent or lawful guardian. Rule 10 explains how to check this: you confirm that the person giving consent is an identifiable adult, using details you already hold, details the parent supplies, or a virtual token from an authorised entity such as DigiLocker.
Moreover, tracking, behavioural monitoring and targeted advertising aimed at children are prohibited, apart from narrow exemptions. Consequently, edtech platforms, schools, gaming apps and hospitals are among the most affected sectors, and they should start planning their parental consent flows early.
Consent Manager vs consent management platform
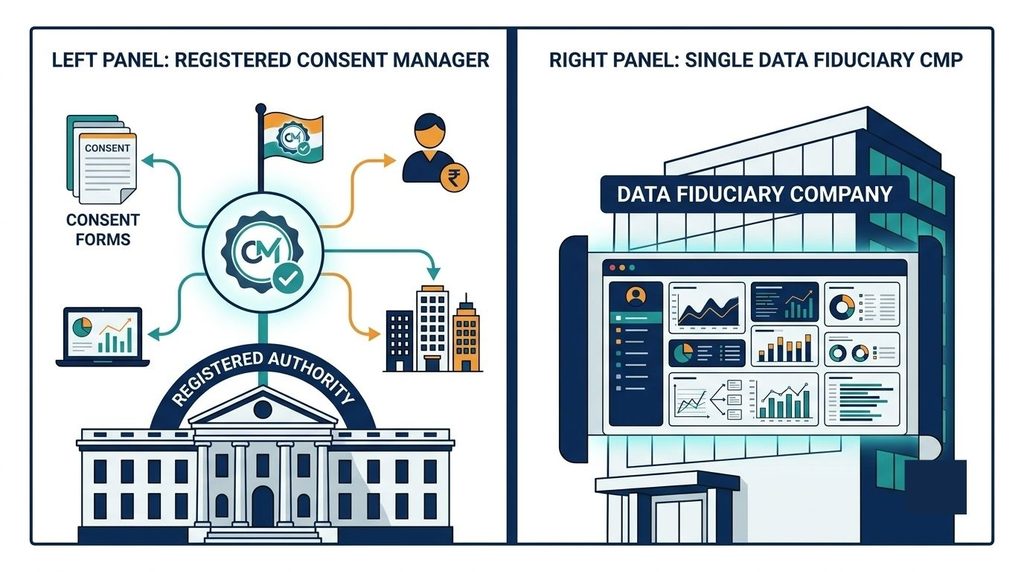
At this point, many readers confuse two similar-sounding terms. The table below separates them clearly.
| Consent Manager | Consent management platform | |
|---|---|---|
| What it is | An entity registered with the Data Protection Board | Software a business runs internally |
| Who it serves | The Data Principal, across many businesses | One Data Fiduciary |
| Registration | Required (Rule 4, from 13 Nov 2026) | Not required |
| Eligibility | An Indian company with a net worth of at least ₹2 crore, plus other conditions | Any vendor can offer it |
| Do you need one? | Optional; you may integrate with one | Practically yes, to capture and prove consent |
In short, a business does not need to become a Consent Manager. Nevertheless, it does need a dependable way to capture consent, sync withdrawals and produce proof. That is exactly the job of a consent management platform.
Penalties for getting consent wrong
The Schedule to the Act sets the maximum penalties that the Data Protection Board can impose.
| Failure | Maximum penalty |
|---|---|
| Failing to take reasonable security safeguards to prevent a breach | ₹250 crore |
| Failing to notify the Board and affected people of a breach | ₹200 crore |
| Failing the additional obligations for children’s data | ₹200 crore |
| Failing the additional obligations of a Significant Data Fiduciary | ₹150 crore |
| Breaching any other provision of the Act or Rules, including notice and consent | ₹50 crore |
These are ceilings, not automatic fines. Even so, they signal how seriously the law treats data protection. In addition, the reputational damage from a public consent failure can easily outlast the penalty itself.
How to set up DPDP consent management: 7 steps
Now that the legal picture is clear, here is a practical path to follow.
- Map your data. First, list every place you collect personal data, every field you collect, and every system it flows into.
- Assign a basis to each purpose. Next, mark each purpose as either consent-based or tied to a named Section 7 legitimate use.
- Rewrite your notices. Then create Rule 3 notices for each purpose, in the languages your customers use, and give each one a version number.
- Fix the capture points. After that, remove pre-ticked boxes and bundled consent. Add purpose-level choices on web, app and offline forms.
- Connect downstream systems. Subsequently, make your CRM, marketing, analytics and partner systems read consent status before they act, and receive withdrawals in real time.
- Set up rights and grievance handling. Likewise, give customers a way to access, correct and erase their data and to raise complaints, backed by a clear response process.
- Test the evidence. Finally, pick ten random customers and try to produce each one’s full consent history in under five minutes. If you cannot, fix that well before May 2027.
This order matters. For example, rewriting notices before you finish data mapping usually leads to vague purposes, and vague purposes lead straight back to invalid consent.
Common mistakes to avoid
Even well-meaning teams stumble in predictable ways. Here are the most frequent ones we see.
- Treating the privacy policy as the notice. A long policy page is not a purpose-by-purpose notice.
- Bundling purposes. Combining service delivery, marketing and analytics into one checkbox breaks the “specific” requirement.
- Forgetting offline channels. Branch forms, agent-assisted sign-ups and call-centre scripts need the same consent discipline as your app.
- Ignoring processors. If a withdrawal does not reach your SMS vendor or your analytics provider, processing continues illegally.
- Keeping no history. Overwriting a consent flag erases the very evidence Section 6(10) demands.
Overall, each of these mistakes is easy to prevent, provided you design for proof from the start rather than patching it in later.
How SecureCMS handles DPDP consent management
SecureCMS is SecureDApp’s DPDP consent management platform. It captures purpose-level consent through OTP on email, SMS and WhatsApp, manages purposes alongside a data catalogue, and handles withdrawal and modification of consent. It also enforces revocation across connected systems, automates data principal rights requests, escalates grievances to the Data Protection Officer, and keeps blockchain-backed audit logs that you can show to a regulator.
Because requirements differ by sector, we have mapped them industry by industry: banks, NBFCs, fintech, insurance, hospitals, ecommerce, SaaS, edtech, schools, HR teams, telecom and ISPs, stock brokers and startups.
Ready to see it in action? Book a SecureCMS demo
Frequently asked questions
What is DPDP consent management?
It is the process of collecting, recording, enforcing and proving a person’s consent to the use of their personal data, as required by India’s Digital Personal Data Protection Act, 2023 and the DPDP Rules, 2025.
When do the DPDP consent rules apply?
The notice and consent rules (Rules 3 and 5 to 16) apply from 13 May 2027. Meanwhile, Consent Manager registration applies from 13 November 2026.
Is a cookie banner enough for DPDP compliance?
No. A cookie banner only covers trackers on a website. DPDP consent covers every purpose and channel, including apps, forms, branches and call centres, and it also needs withdrawal sync and proof records.
Do I need to register as a Consent Manager?
No. Registration is meant only for companies that want to act as Consent Managers for Data Principals. A business that handles its own customers’ data needs consent management, not registration.
Can a customer withdraw consent and still use my service?
Yes, provided the service does not depend on the withdrawn purpose. For example, withdrawing marketing consent cannot stop someone from using their bank account or completing an order.
What is the penalty for not following DPDP consent rules?
Up to ₹50 crore for general notice and consent failures, and up to ₹250 crore for failing to take reasonable security safeguards that lead to a breach.
Final thoughts
To sum up, DPDP consent management is not a one-time legal exercise. Rather, it is an ongoing operating process that touches product, marketing, engineering, legal, and customer support. Because the main obligations begin on 13 May 2027, the most sensible approach is to start now: map your data, fix your notices, connect your systems and test your evidence. Do these four things, and the rest of the compliance journey becomes far more manageable.
This article summarises the law for general information and is not legal advice. Please consult a qualified legal professional for your specific situation.